
Artificial intelligence (AI) is changing how businesses communicate, manage information and protect their digital operations. However, the same technology that helps organisations improve productivity is also giving cybercriminals new ways to deceive employees, impersonate trusted contacts and exploit weaknesses in business systems.
A development published by Microsoft on 28 October 2026 highlights an increasingly important cybersecurity challenge: traditional warning signs, such as spelling mistakes, suspicious wording and poorly designed emails, are becoming less reliable indicators of fraud.
According to Microsoft’s latest digital security findings, cybercriminals are using AI to produce convincing messages, imitate communication styles and scale social engineering campaigns. The company reports that 73.3% of observed cyberattack attempts involved user interaction, valid account abuse, social engineering and phishing. Microsoft also detected more than 46 million identity impersonation attacks through business email. Source Asia+1
For businesses, the implications extend beyond the IT department. Employees handling invoices, customer records, supplier communications and confidential information can all become targets. A single compromised account may provide an attacker with an opportunity to access additional systems or sensitive business data.
Why AI is changing the cybersecurity landscape
Phishing remains a familiar threat, but AI can make fraudulent communications more personalised and convincing. Attackers may imitate the tone of a manager, create realistic supplier requests or construct messages that appear to belong to legitimate service providers.
The challenge is that employees can no longer rely on how a message looks or sounds to determine whether it is genuine. Instead, organisations need processes that independently verify identity, access requests and financial instructions.
Microsoft’s 2026 Digital Defense Report also describes a changing threat environment in which AI is assisting activities such as reconnaissance, social engineering, vulnerability discovery and malware development. While human involvement remains significant in many real-world attacks, automation can accelerate parts of the process.
Businesses must therefore combine technical safeguards with practical changes in employee behaviour.
Five digital habits businesses must change
1. Stop trusting messages simply because they look legitimate
A professional email, familiar logo or convincing writing style does not guarantee authenticity. Employees should be cautious when messages unexpectedly request confidential information, password resets, urgent payments or changes to supplier banking details.
For sensitive requests, verification should take place through a separate, trusted communication channel. For example, an employee should call a known supplier contact using an existing telephone number rather than relying on the contact details contained in a suspicious email.
2. Verify links and attachments before opening them
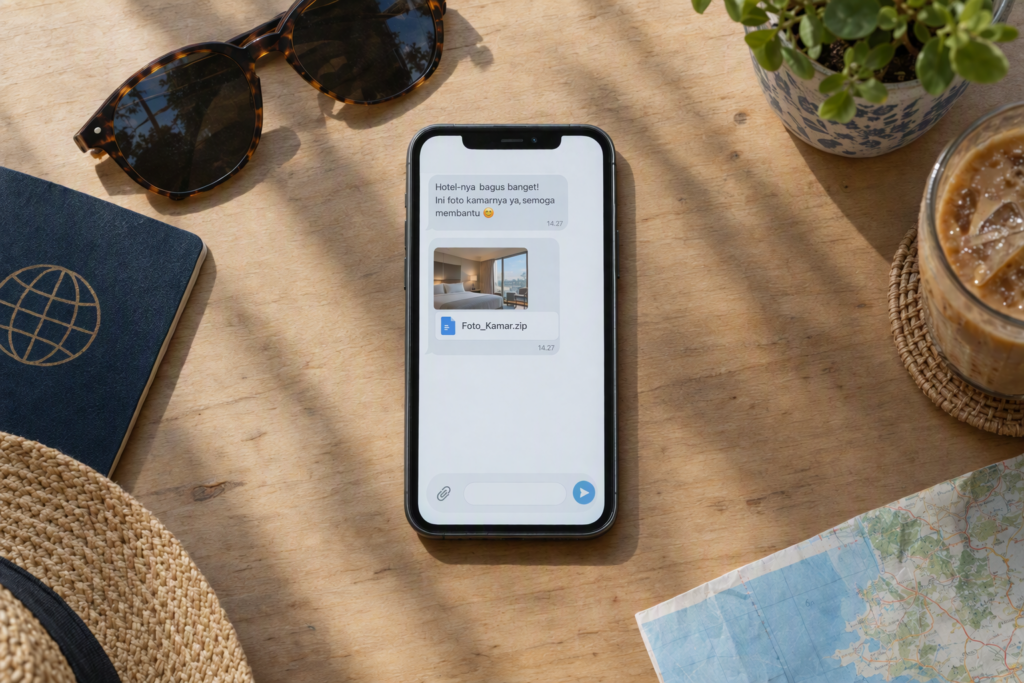
Unexpected files and links remain common ways for attackers to gain access to devices and business networks. A document that appears to contain an invoice, booking confirmation or customer photograph may lead to a malicious download or fraudulent website.
Employees should avoid opening unexpected attachments without confirming their origin. Businesses should also maintain updated security software, apply available software patches and use email filtering to help identify dangerous links and files.
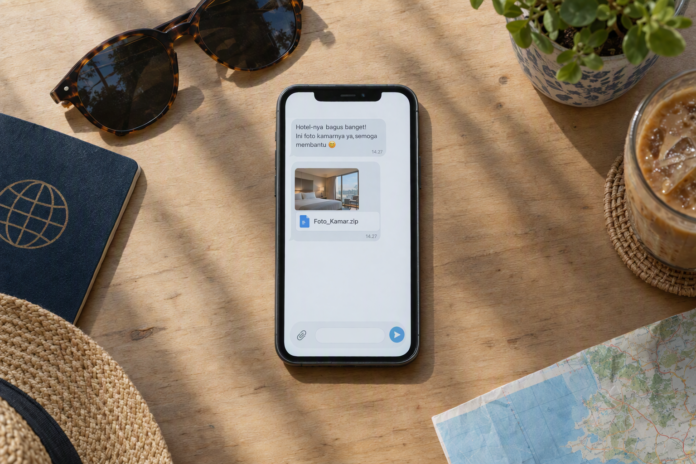
Microsoft has previously documented a campaign known as Photo.zip, which used deceptive messages and files disguised as photographs to target hospitality organisations. The example demonstrates how ordinary business activities can become opportunities for cyberattacks. Source Asia
3. Treat QR codes and digital documents with caution
QR codes are widely used for payments, event registrations, document sharing and customer services. However, a QR code can direct a user to a fraudulent website designed to collect login details or other sensitive information.
Before scanning a code, employees should consider whether it comes from a trusted source and inspect the destination before entering information. The same caution applies to PDF documents, digital forms and verification pages.
Businesses can reduce exposure by providing approved links through official channels and educating staff about fraudulent redirects and imitation login pages.
4. Protect digital identities, not just devices
Cybersecurity strategies often focus on computers, networks and antivirus software. Yet employee identities and access credentials are equally important.
Email accounts, cloud applications, customer databases and collaboration platforms can contain valuable information. If an attacker gains access to one account, they may attempt to use that access to reach other systems.
Businesses should provide employees with unique passwords, remove unnecessary account permissions and promptly revoke access when staff change roles or leave the organisation. Monitoring unusual sign-ins and reviewing access privileges can also help identify suspicious activity.
5. Strengthen authentication and control AI access
Passwords alone offer limited protection when credentials are stolen or exposed. Organisations should enable multi-factor authentication (MFA), prioritising phishing-resistant methods where available, and consider passkeys on supported services.
Companies should also review how employees use AI assistants and autonomous AI agents. These tools may access files, business applications or confidential information to complete tasks. Giving them excessive permissions can increase the consequences of mistakes, misuse or compromised accounts.
Access should be restricted to what each tool genuinely needs, with human approval for sensitive actions such as transferring funds, changing account permissions or sharing confidential records.
Building a stronger cybersecurity culture
The responsibility for digital security cannot rest with technology teams alone. Managers, finance departments, human resources professionals and frontline employees all influence how effectively an organisation identifies and responds to threats.
Regular training should use realistic examples of fraudulent supplier requests, impersonation attempts and suspicious login pages. Businesses should also establish clear reporting procedures so employees can raise concerns without fear of blame.
Importantly, AI can support defensive security by helping teams analyse activity, identify unusual patterns and prioritise potential threats. However, automated tools should operate within clear permissions and oversight arrangements.
For South African businesses, these measures are particularly relevant wherever organisations process customer information, employee records, financial transactions or confidential commercial data.
Conclusion: Small habits can prevent major incidents
AI is not making every cyberattack sophisticated, nor does every unusual email indicate fraud. The greater challenge is that attackers can use technology to make deception more convincing and repeat it at greater scale.
Businesses that verify unusual requests, protect employee identities, strengthen authentication and carefully manage AI access can reduce avoidable risks.
As organisations adopt more AI-powered tools, cybersecurity must evolve alongside innovation. The most effective defence combines reliable technology, clear procedures and employees who understand that familiar-looking digital communications are not always trustworthy.